Introduction
In the digital age, data has become the lifeblood of modern businesses. As companies generate and store vast amounts of data (big data), the need for efficient and secure data storage solutions has never been greater.
Data lakes have emerged as one such solution, allowing organizations to store, manage, and analyze large and varied datasets.
However, with the benefits of data lakes come significant security risks. Cyber attacks and data breaches have become increasingly common, and organizations must take necessary steps to secure their data lakes.
In this DataSec article, we’ll provide a checklist for ensuring the security of data lakes, highlighting the key security measures that organizations must implement to protect their data.
What is a Data Lake?
A data lake is a centralized repository that allows organizations to store and manage large volumes of structured and unstructured data.
Unlike traditional storage, data lakes accept data from many sources, such as IoT devices and customer databases.
Data lakes support advanced analytics, machine learning, and AI on large, diverse datasets.
Data lakes are typically built using cloud computing technologies, enabling organizations to scale their storage capacity quickly and efficiently.
Teams can store data in its native format, which adds flexibility and eases processing.
However, data lakes often connect to the internet and hold sensitive data, so attackers target them.
Therefore, organizations must secure their data lakes and monitor them for threats.
Access Control, Authorization, and Authentication
Access control is one of the most critical security measures for any data storage system, including data lakes.
In practice, this means only people with the right permissions can access data in the lake.
To implement effective access control, two key components are necessary: authentication and authorization.
Authentication ensures that the person trying to access the data is who they claim to be. Authorization, on the other hand, determines whether the user has the necessary permissions to access the data.
By default, organizations often give many employees access to cloud platforms and data lakes, which creates needless risk. Therefore, implementing a well-guarded access control system is essential to restrict access to only authorized personnel.
An effective system verifies who has access and limits it to a small group. This helps to prevent unauthorized access and protect the data stored in the data lake.
Platform Hardening
Platform hardening is another critical measure for ensuring data lake security. It involves minimizing the potential “attack surface” of the system, which refers to the number of ways that an attacker could exploit a vulnerability in the system to gain access to sensitive data.
To harden the platform, remove unnecessary cloud tools, ports, applications, and services.
Also, restrict access to the data lake and configure access controls for resources. If the data lake sits on the cloud, create only one cloud account for deployments.
Moreover, it’s essential to incorporate security standards and guidelines listed by the Computer Information Security (CIS) Center for Internet Security and other standardized data security boards.
By following these guidelines, organizations can ensure their data lake is secure and protect against common attack vectors.
As a result, platform hardening makes the data lake harder to attack.

Data Lineage
Data lineage refers to the process of tracking the movement of data within a data lake. In a data lake, data comes from various sources and is stored in its raw form. This makes it challenging to keep track of where the data is coming from, how it’s being used, and where it’s going.
Data lineage creates a map of the data, enabling organizations to track the data’s flow and identify any risks or gaps within the data lake.
With data lineage, organizations can know when, by whom, and where the data is moving/accessed. This helps track the data flow and identify any risks or gaps within the data lake.
Data lineage is essential in identifying the origin of data, identifying who has access to it, and how it’s being used.
By keeping track of data lineage, organizations can prevent unauthorized data access and ensure data accuracy and completeness. Additionally, data lineage helps organizations to comply with data protection regulations and meet auditing requirements.
Host-Based Security
Host-based security is a security measure that involves securing the host system, including servers and endpoints. It involves implementing intrusion detection algorithms, audit trails, and log management to detect any unusual activity or access requests.
Intrusion detection algorithms identify anomalous activities or access requests and notify the relevant authorities.
These activities may be internal, coming from within the organization’s network, or external, coming from an external attacker.
By implementing intrusion detection algorithms at the host level, organizations can detect anomalous activities and prevent unauthorized access to the data stored in the data lake.
Log management and intrusion detection algorithms are both critical components of host-based security. Collecting and managing logs can be exhaustive on resources such as storage.
Therefore, having an intrusion detection system can help detect anomalies without taking up resources.
Together, intrusion detection, log management, and host-based controls protect the data lake.
Implement RBAC & IAM Solutions
Implementing Role-Based Access Control (RBAC) and Identity and Access Management (IAM) solutions is another critical measure for ensuring data lake security.
RBAC involves defining user roles and permissions based on their job responsibilities. It enables organizations to restrict access to specific resources based on the roles and responsibilities of individual users.
By using RBAC, organizations can control access to sensitive data and prevent unauthorized access.
IAM, on the other hand, involves managing user identities and their access to resources. It enables organizations to grant, revoke, or modify user permissions based on their role and responsibilities.
IAM solutions typically involve multi-factor authentication, which adds an additional layer of security to the system.
Implementing RBAC and IAM solutions is critical in large organizations with multiple departments and varied job roles. It enables organizations to control access to specific resources and prevents unauthorized data access.
Together, RBAC, IAM, and other controls keep the data lake secure.
Data Encryption
Data encryption is another crucial security measure for ensuring data lake security. Encryption involves encoding data using a specific algorithm and key, making it unreadable to anyone without access to the key.
If an unauthorized user gains access to encrypted data, they will not be able to read it without the encryption key. Data encryption provides a layer of security against malicious attacks, data breaches, and other cyber threats.
For data lakes that sit on the cloud, it’s essential to follow the encryption guidelines recommended (and in most cases, provided) by the cloud service provider. Secure on-prem data lakes with encryption policies from standard security bodies.
Encryption can be done at all levels of data storage systems, such as files, tools, applications, and databases. As a result, encrypted data stays protected even if intruders reach it.
Combined with RBAC, IAM, and access control, encryption provides a robust protection layer.
Network Perimeter
Network perimeter security is another critical security measure for ensuring data lake security. In practice, this means protecting the organization’s network with strong security protocols to prevent cyber threats and restrict hackers.
Firewalls are an essential component of network perimeter security. They act as sieves, allowing only certain traffic to flow into the organization’s network, which helps to restrict the flow of traffic that might potentially harm the network.
Intrusion detection and prevention algorithms are also an efficient way of identifying and restricting anomalous events. They use advanced machine learning algorithms to identify threat profiles or activities and notify the relevant authorities.
Teams can also use border routers, VPNs, and network segmentation to secure the perimeter.
By securing the network perimeter, organizations can prevent unauthorized access to the data lake and protect it from cyber threats.
In summary, securing the network perimeter is critical for protecting the organization’s data lake.
Firewalls, intrusion prevention, and other perimeter controls complete the protection.
Data Lake Security Checklist
To summarize the key points discussed, here’s a data lake security checklist that organizations should consider to ensure their data lake is secure:
Access Control, Authorization, and Authentication: Implement access control protocols to identify and verify “who” has access to the data lake and restrict access to limited people.
1. Platform Hardening
Remove unnecessary cloud tools, ports, applications, and services connected to the data lake. Configure access controls for resource access and allocation.
Follow security standards and guidelines listed by the Computer Information Security (CIS) Center for Internet Security and other standardized data security boards.
2. Data Lineage
Keep track of where the data is originating, how and who is using it, its movement in the data lake, and so on. Data lineage creates a map of the data, enabling organizations to track the data flow and identify any risks or gaps within the data lake.
3. Host-Based Security
Implement intrusion detection algorithms, audit trails, log management, and other measures to secure the host system and detect anomalous activities or access requests.
Implement RBAC & IAM solutions to grant access and keep track of resource controls.
4. Data Encryption
Encrypt data at all levels of data storage systems to protect it from unauthorized access.
5. Network Perimeter
Secure the network perimeter with firewalls, intrusion detection and prevention algorithms, and other measures to prevent cyber threats and restrict hackers.
By following this checklist, organizations can ensure that their data lake is secure and protected from cyber threats, unauthorized access, and data breaches.
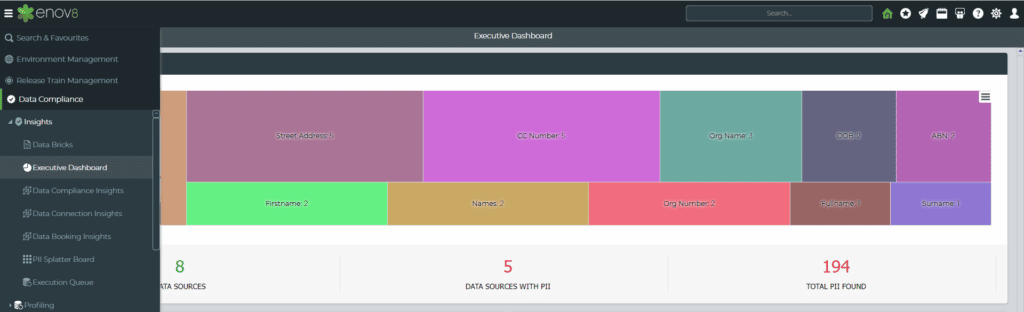
Enov8: Manage your IT Landscape: Risk Screenshot
Leveraging Enov8
Enov8 offers comprehensive solutions to help manage your IT footprint & data security concerns, including its IT Environment Management and Test Data Management solutions.
Enov8 Environment Manager enables organizations to gain a better understanding of their IT landscape and manage it more effectively. Its out-of-the-box modeling capabilities, coupled with system security information capture, facilitate planning, coordination, and incident management.
Additionally, it offers orchestration through automation and provides real-time insights across the IT fabric. By leveraging Enov8 Environment Manager, organizations can streamline their IT operations, enhance system security, and improve their overall IT performance.
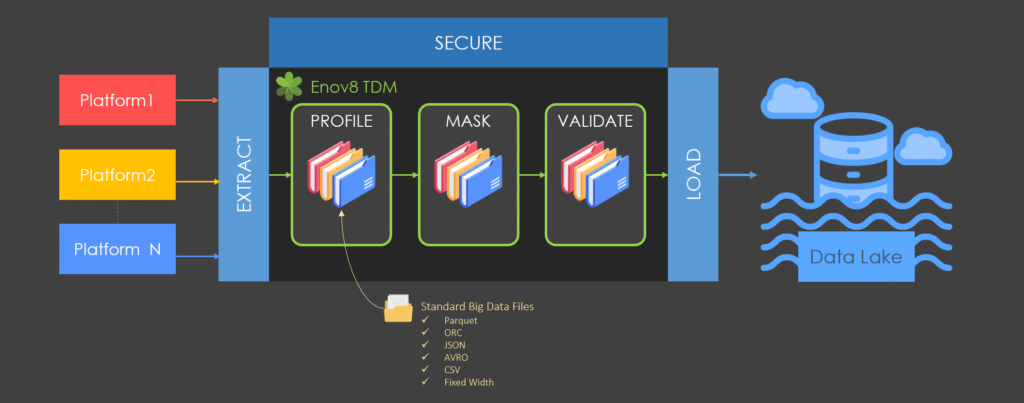
Enov8 Test Data Manager (aka Data Compliance Suite) is another solution that complements the needs of data security and data privacy by providing data profiling for risk discovery, data masking for obfuscation, and compliance validation methods.
By leveraging Enov8 Test Data Manager in conjunction with Enov8’s IT environment management and data security platform, organizations can further strengthen their data security measures and protect their data more effectively.
Conclusion
In conclusion, the exponential growth of data generation has made data storage repositories such as data lakes and cloud computing technologies indispensable for organizations.
However, data security has become a major concern for organizations as cyber threats and data breaches have become increasingly common.
To mitigate these risks, organizations must take measures to ensure their data lakes are secure and functional at all times.
The checklist provided above, covering access control, platform hardening, data lineage, host-based security, RBAC and IAM solutions, data encryption, and network perimeter, serves as a comprehensive guide for securing data lakes.
Furthermore, leveraging platforms such as Enov8 can enable organizations to manage their IT environments and data security more effectively.
Enov8 provides a centralized platform for IT environment management and data security, enabling organizations to gain a comprehensive view of their IT environment, plan and coordinate changes more effectively, automate their IT environment and data changes, and protect their data from cyber threats.
Overall, securing data lakes is essential for building a strong development and deployment pipeline, which is crucial for business growth. Therefore, organizations must prioritize data security and implement the right measures and security policies to protect their data.
Other Data Reading
Enov8 Blog: What is Data Friction from the Perspective of TDM
Enov8 Blog: What is Data Masking? And how do we do it?
Enov8 Blog: A DevOps Approach to Test Data Management
Author Andrew Walker
Andrew Walker is a software architect with 10+ years of experience. Andrew is passionate about his craft, and he loves using his skills to design enterprise solutions for Enov8, in the areas of IT Environments, Release & Data Management.